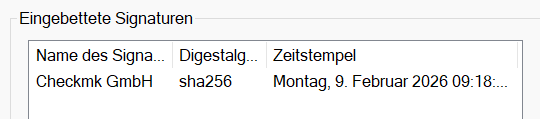
our security solution recently flagged check_mk_agent.exe for accessing lsass.exe on a Windows host. We’ve been trying to figure out whether this is expected behavior or something to be concerned about.
A few things caught our attention: The alert additionally mentions that the process module is “not clean and not signed”. We’re running the official Checkmk Raw Edition with the standard agent package downloaded directly from the Checkmk server.
Our questions:
Has anyone seen check_mk_agent.exe access lsass.exe? Could this be a side effect of the agent running under SYSTEM privileges?
Should the official Raw Edition agent binary always carry a valid signature?
Has anyone dealt with a similar alert and found a clear root cause?
No. At least not a special one, only the defaults that come with checkmk.
The weird part is: My check_mk_agent.exe also has a valid Signature. That is why I created this post, because we couldn’t explain this “unauthorized access”.
I’m unsure why this issue is not gaining more attention. We are seeing this behavior too. Before blindly adding an exemption rule in our system to allow the behavior, I’d like to know why the check_mk_agent.exe (which is signed and trusted) is trying to access the c:\windows\system32\lsass.exe process. This action is classified as credential stealing behavior by accessing the local security authority subsystem and the activity rightfully blocked. The monitoring agent is otherwise working so the access is non-blocking.
@andreas-doehler you know more about Windows than I do. But I’d assume that the origin of that comes via the process check (ps). The process check needs information on all processes and accesses as such all running processes to read process owner and memory usage etc.
The reason why this does not make any impact in the monitoring. By default processes don’t appear in your monitoring, only when you want them to be explicitely be monitored. Otherwise it would spam your monitoring with thousands of services, which you probably dont care about