Error message:Unable to create authentication request
Please contact your administrator.
Output of “cmk --debug -vvn hostname”: (If it is a problem with checks or plugins)
Hello,
I have setup SAML with Azrue via the webui in a previous version (some of 2.3.0) which always worked flawlessly.
Today I updated to 2.4.0 and SAML does not work anymore.
Error:
Unable to create authentication request
Please contact your administrator.
In /var/log/webserver.log I also found this error message:
Thanks. Can you raise the log_level to Debug and share the ~/var/log/web.log ?
If its possible to open a support ticket, then we can also handle it there.
Sadly, we don’t have support
But I will propose it at our next renewal
I’ve set Alerts and Core to debug and exported the log.
Here is a redacted version:
2025-05-07 12:38:46,599 [10] [cmk.web.saml2 124234] Accessing SAML2.0 connector
2025-05-07 12:38:46,600 [10] [cmk.web.saml2 124234] Authentication request to Identity Provider REDACTED at URL Entra Single Sign-On (REDACTED)
2025-05-07 12:38:46,600 [10] [cmk.web.saml2 124234] Authentication request with RelayState=REDACTED,index.py
2025-05-07 12:38:46,638 [10] [saml2.httpbase 124234] GET to https://login.microsoftonline.com/IDREDACTED/federationmetadata/2007-06/federationmetadata.xml?appid=IDREDACTED
2025-05-07 12:38:46,639 [10] [urllib3.connectionpool 124234] Starting new HTTPS connection (1): login.microsoftonline.com:443
2025-05-07 12:38:46,868 [10] [urllib3.connectionpool 124234] https://login.microsoftonline.com:443 "GET /IDREDACTED/federationmetadata/2007-06/federationmetadata.xml?appid=IDREDACTED HTTP/11" 200 4729
2025-05-07 12:38:46,869 [10] [saml2.httpbase 124234] Response status: 200
2025-05-07 12:38:46,872 [10] [saml2.assertion 124234] policy restrictions: None
2025-05-07 12:38:46,910 [10] [saml2.mdstore 124234] service(https://sts.windows.net/IDREDACTED/, idpsso_descriptor, single_sign_on_service, urn:oasis:names:tc:SAML:2.0:bindings:HTTP-POST)
2025-05-07 12:38:46,910 [10] [saml2.mdstore 124234] service => [{'__class__': 'urn:oasis:names:tc:SAML:2.0:metadata&SingleSignOnService', 'binding': 'urn:oasis:names:tc:SAML:2.0:bindings:HTTP-POST', 'location': 'https://login.microsoftonline.com/IDREDACTED/saml2'}]
2025-05-07 12:38:46,971 [10] [cmk.web.saml2 124234] Prepare authentication request
2025-05-07 12:38:46,971 [10] [saml2.entity 124234] REQUEST: <ns0:AuthnRequest xmlns:ns0="urn:oasis:names:tc:SAML:2.0:protocol" xmlns:ns1="urn:oasis:names:tc:SAML:2.0:assertion" xmlns:ns2="http://www.w3.org/2000/09/xmldsig#" ID="id-IDREDACTED" Version="2.0" IssueInstant="2025-05-07T10:38:46Z" Destination="https://login.microsoftonline.com/IDREDACTED/saml2" ProtocolBinding="urn:oasis:names:tc:SAML:2.0:bindings:HTTP-POST" AssertionConsumerServiceURL="https://checkmk.REDACTED.de/REDACTED/check_mk/saml_acs.py?acs"><ns1:Issuer Format="urn:oasis:names:tc:SAML:2.0:nameid-format:entity">https://checkmk.REDACTED.de/REDACTED/check_mk/saml_metadata.py</ns1:Issuer><ns2:Signature Id="Signature1"><ns2:SignedInfo><ns2:CanonicalizationMethod Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#" /><ns2:SignatureMethod Algorithm="http://www.w3.org/2001/04/xmldsig-more#rsa-sha256" /><ns2:Reference URI="#id-IDREDACTED"><ns2:Transforms><ns2:Transform Algorithm="http://www.w3.org/2000/09/xmldsig#enveloped-signature" /><ns2:Transform Algorithm="http://www.w3.org/2001/10/xml-exc-c14n#" /></ns2:Transforms><ns2:DigestMethod Algorithm="http://www.w3.org/2001/04/xmlenc#sha256" /><ns2:DigestValue /></ns2:Reference></ns2:SignedInfo><ns2:SignatureValue /><ns2:KeyInfo><ns2:X509Data><ns2:X509Certificate>CERTREDACTED</ns2:X509Certificate></ns2:X509Data></ns2:KeyInfo></ns2:Signature><ns0:NameIDPolicy Format="urn:oasis:names:tc:SAML:1.1:nameid-format:unspecified" AllowCreate="false" /></ns0:AuthnRequest>
2025-05-07 12:38:46,975 [10] [saml2.sigver 124234] xmlsec command: /omd/sites/REDACTED/bin/xmlsec1 --sign --privkey-pem /omd/sites/REDACTED/etc/ssl/saml2/custom/REDACTED/signature/private.pem --id-attr:ID urn:oasis:names:tc:SAML:2.0:protocol:AuthnRequest --node-id id-IDREDACTED --output /tmp/tmpsdp2327g.xml --lax-key-search /tmp/tmptmcsxf0i.xml
2025-05-07 12:38:47,000 [40] [saml2.sigver 124234] returncode=1
error=Signature status: ERROR
Error: failed to sign file "/tmp/tmptmcsxf0i.xml"

output=
2025-05-07 12:38:47,000 [30] [cmk.web.saml2 124234] Entra Single Sign-On (REDACTED) - SignatureError: ['/omd/sites/REDACTED/bin/xmlsec1', '--sign', '--privkey-pem', '/omd/sites/REDACTED/etc/ssl/saml2/custom/REDACTED/signature/private.pem', '--id-attr:ID', 'urn:oasis:names:tc:SAML:2.0:protocol:AuthnRequest', '--node-id', 'id-IDREDACTED', '--output', '/tmp/tmpsdp2327g.xml', '--lax-key-search', '/tmp/tmptmcsxf0i.xml']
2025-05-07 12:38:47,000 [10] [cmk.web.saml2 124234] Unable to create authentication request
Traceback (most recent call last):
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/sigver.py", line 796, in sign_statement
    (stdout, stderr, output) = self._run_xmlsec(com_list, [tmp.name])
                               ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/sigver.py", line 870, in _run_xmlsec
    raise XmlsecError(errmsg)
saml2.sigver.XmlsecError: returncode=1
error=Signature status: ERROR
Error: failed to sign file "/tmp/tmptmcsxf0i.xml"

output=

The above exception was the direct cause of the following exception:

Traceback (most recent call last):
  File "/omd/sites/REDACTED/lib/python3/cmk/gui/cee/saml2/_pages.py", line 131, in page
    authentication_request = interface.authentication_request(relay_state_string)
                             ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3/cmk/gui/cee/saml2/_interface.py", line 264, in authentication_request
    authn_request_id, authn_request = self._client.create_authn_request(
                                      ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/client_base.py", line 446, in create_authn_request
    msg = self._message(
          ^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/entity.py", line 588, in _message
    signed_req = self.sign(
                 ^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/entity.py", line 524, in sign
    return signed_instance_factory(msg, self.sec, to_sign)
           ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/sigver.py", line 331, in signed_instance_factory
    signed_xml = seccont.sign_statement(signed_xml, node_name=node_name, node_id=nodeid)
                 ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/sigver.py", line 1695, in sign_statement
    return self.crypto.sign_statement(
           ^^^^^^^^^^^^^^^^^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3.12/site-packages/saml2/sigver.py", line 798, in sign_statement
    raise SignatureError(com_list) from e
saml2.sigver.SignatureError: ['/omd/sites/REDACTED/bin/xmlsec1', '--sign', '--privkey-pem', '/omd/sites/REDACTED/etc/ssl/saml2/custom/REDACTED/signature/private.pem', '--id-attr:ID', 'urn:oasis:names:tc:SAML:2.0:protocol:AuthnRequest', '--node-id', 'id-IDREDACTED', '--output', '/tmp/tmpsdp2327g.xml', '--lax-key-search', '/tmp/tmptmcsxf0i.xml']

The above exception was the direct cause of the following exception:

Traceback (most recent call last):
  File "/omd/sites/REDACTED/lib/python3/cmk/gui/cee/saml2/_pages.py", line 151, in handle_page
    post_request = self.page()
                   ^^^^^^^^^^^
  File "/omd/sites/REDACTED/lib/python3/cmk/gui/cee/saml2/_pages.py", line 139, in page
    raise MKUserError(
cmk.gui.exceptions.MKUserError: Unable to create authentication request
2025-05-07 12:38:47,002 [10] [cmk.web 124234] Disconnecting site connections
2025-05-07 12:38:47,002 [10] [cmk.store 124234] Releasing all locks
2025-05-07 12:38:47,002 [10] [cmk.store 124234] Acquired locks: {}
2025-05-07 12:38:47,002 [10] [cmk.store 124234] Releasing all locks
2025-05-07 12:38:47,002 [10] [cmk.store 124234] Acquired locks: {}
I pretty much never modified any files manually, only installed some Extension Packages.
Also I once renewed the certificate manually via SSH since I didn’t know at the time yet, that it is possible to renew it via webconf.
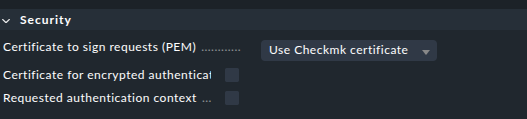
I switched to the Checkmk cert and it works!
Previously I generated one internally and uploaded that to Azure and put it in the SAML config.
Thank you for the help, if it works that way I will leave it as is.
Or are there any security risks if I use the cert of Checkmk?
Greetings
Max
Previously I generated one internally and uploaded that to Azure and put it in the SAML config.
(The one I uploaded to Azure is from our internal AD CS, which is trusted by Checkmk)
As per the inline help:
Checkmk signs your SAML 2.0 requests to your identity provider. You can use the certificate that comes with Checkmk. Alternatively, if your organization manages its own certificates, you can add a custom certificate. Note that the public certificate must be a single certificate (not a certificate chain). Only RSA certificates are supported at this time.
So, in principle custom certificates should work if it matches the above criteria. If you could try this on a freshly created test site, then this will help to nail down the problem ?